ASUS high severity vulnerability, update now

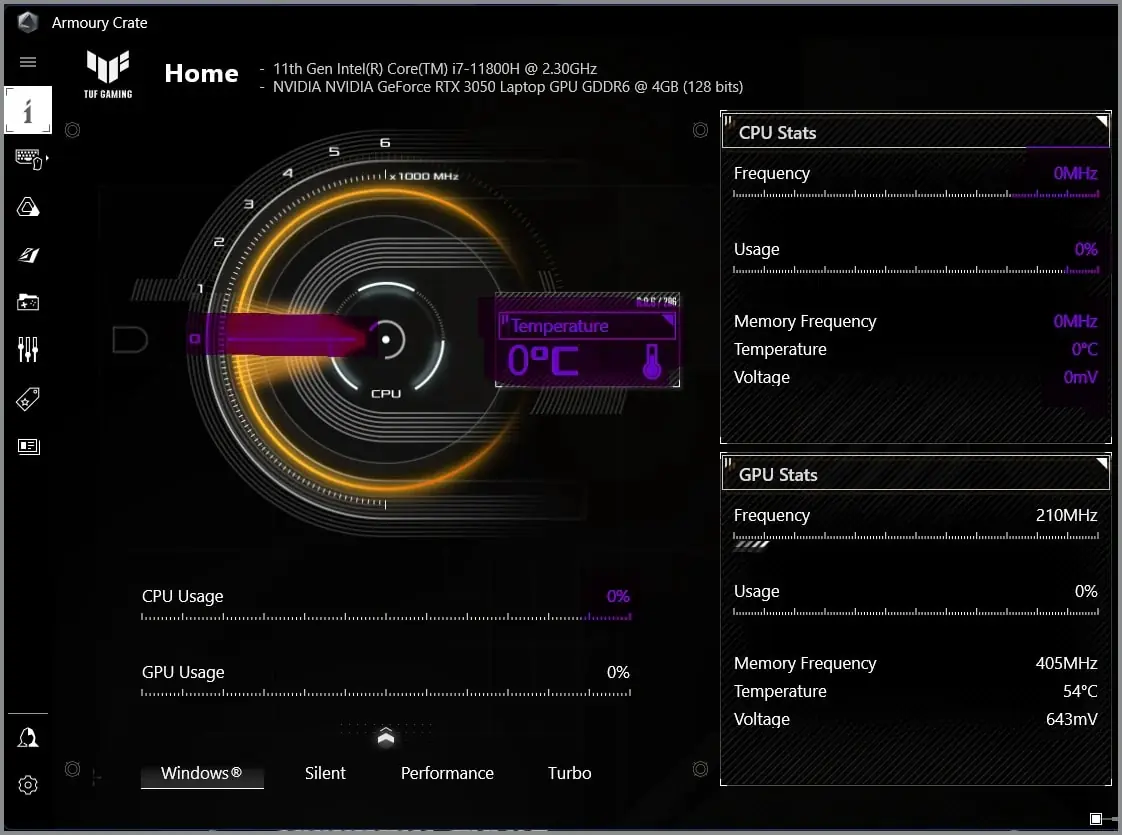
Armoury Crate is a centralized application developed by ASUS to manage and customize the settings of ASUS hardware and peripherals. It provides users with a unified interface to control various functions, such as RGB lighting, system performance, fan speeds, and device configurations.
In this software, Talos identified the vulnerability CVE-2025-3464 in the AsIO3.sys driver. The AsIO3.sys driver builds Asusgio3. The vulnerability, which is classified as High severity, is caused by a race condition (time-of-check-time-of-use problem) in the AsIO3.sys file. This could lead to authentication bypass.

See more articles from iGuRu.gr when you search for news on Google.

According to Talos , a specially crafted link can lead to authorization bypass. This affects the AsIO3.sys file of Asus Armoury Crate 5.9.13.0. According to ASUS, the vulnerability, CVE-2025-3464, affects software versions between V5.9.9.0 and V6.1.18.0.

ASUS has released an update for its Armoury Crate system management software as of June 16, 2025, according to this website.

This update contains important security updates and ASUS strongly recommends that users update their Armoury Crate installation to the latest version.

You can install the update by opening Armoury Crate in the Settings > Update Center tab and clicking Check for updates. Then select “Update in ARMOURY CRATE”.


Google preferences

Leave a Comment

Your email address will not be published. Required fields are marked *

Your message will not be published if:
1. Contains insulting, defamatory, racist, offensive or inappropriate comments.
2. Causes harm to minors.
3. It interferes with the privacy and individual and social rights of other users.
4. Advertises products or services or websites.
5. Contains personal information (address, phone, etc.).