The ads on your phone are hiding something more dangerous

There are various malicious programs that can "hole" your mobile. For example, some spyware that can turn your mobile into a "bug". Or a Trojan that tricks the user and steals information such as bank codes or credit card numbers. Or even ransomware, which locks the device and demands a ransom to use it again.

And there's a more innocent-looking threat: adware. "It displays unwanted ads, but behind it lies serious dangers," warns Phil Muncaster of cybersecurity firm ESET, adding that according to ESET's latest report (pdf), adware incidents increased by an alarming 160% in the first half of 2025.

See more articles from iGuRu.gr when you search for news on Google.

But what is adware and how does it work?

Not all adware is illegal. In its most "innocent" form, it can be a free program that legitimately displays ads that are not easily disabled. Annoying, but not necessarily dangerous.

However, there is also a darker side: so-called potentially unwanted applications (PUA/PUP).

These:

  • fill your device with annoying ads,
  • change settings without permission,
  • and in more serious cases, steal personal data.

Generally, the term adware refers to any unwanted or malicious software that displays advertisements on your device without your consent.

Ads may appear as:

  • pop-up windows
  • in-browser ads
  • advertising banners
  • push notifications
  • full-screen content, even video

The goal of adware is to trick you into viewing or clicking on ads, and ultimately make a profit, sometimes even by stealing money or data.

Additionally, these types of threats can:

  • monitor what you do online and show you "cut and sewn" ads
  • steal your personal information and sell it to others
  • automatically click on ads without you knowing, so that scammers can make money
  • hide on the phone after installation, so you can't easily delete them
  • "eat" your data package
  • to make the mobile phone work slower
  • to pave the way for more dangerous malware


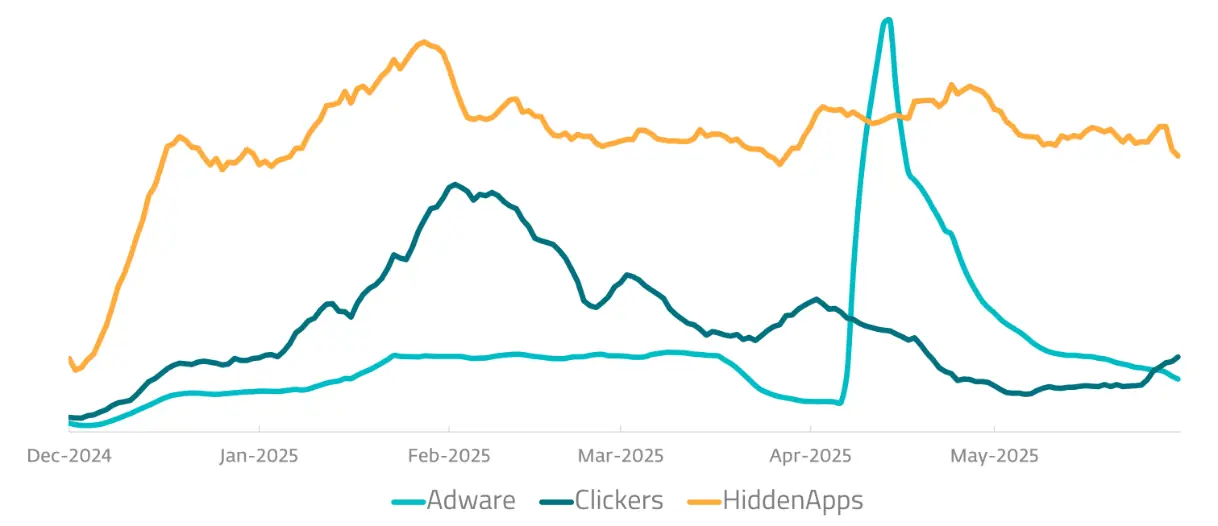
Android Adware, Clicker, and HiddenApp Detections in the Second Half of 2024 and the First Half of 2025 (Source: ESET Threat Report 1ο Semester 2025)
How does it infiltrate your device?

Adware creators are constantly finding ways to trick users. Some of the most common ones are:

  • to present it as a normal application,
  • to "package" it with free programs,
  • exploit weaknesses in the mobile phone or its software,
  • trick you into clicking on suspicious or fake ads,
  • show misleading pop-ups (e.g. "your device is infected!"),
  • send malicious links via email, SMS or social networks.

How do they manage to escape?

Adware creators do everything they can to avoid detection. They often hide it inside “legitimate” freeware or present it as a system update. In fact, they make sure to constantly change it so that it escapes protection programs.

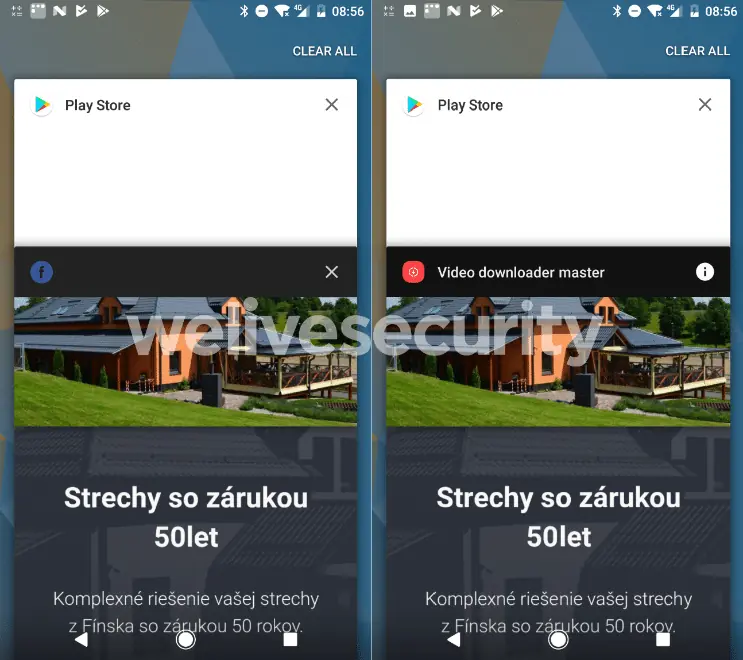
Fake Facebook app : adware that tricks users (Source: ESET research )

Introducing Kaleidoscope​

A particularly sophisticated adware variant recently detected by ESET is called Kaleidoscope. It is an adware campaign targeting Android devices that uses the “evil twin” tactic. In this, the creators release two identical versions of the same application: a harmless one published in the official app store, and a malicious one distributed through unofficial third-party stores. Deceptive advertisements direct victims to the second one.

Most worryingly, both versions have the same name and app ID. This means that malicious ads produced by the illegal version are recognized by advertisers as legitimate. This way, cybercriminals generate revenue, while victims are inundated with ads that slow down their devices.

The data is revealing: adware was responsible for more than a quarter (28%) of all adware detections on Android in the first half of 2025.

Has adware entered my device?

If you notice any of the following signs on your Android phone, adware may be installed:

  • The phone is slow or hangs frequently.
  • Unknown apps, extensions, or toolbars appear.
  • Web pages don't load properly.
  • They bombard you with excessive advertising.
  • The browser's home page changes without your permission.
  • The battery runs out very quickly.
  • Your package data is being consumed for no reason.

How to avoid it

Fortunately, you can significantly reduce the risk of adware by paying attention to the following:

  1. Only download applications from Google Play Store and avoid unofficial app stores.
  2. Always check who the creator is and read the reviews before installing.
  3. Don't click on suspicious ads or pop-ups as they may be malicious.
  4. Keep your mobile updated (operating system and browser) to ensure that there are no vulnerabilities that could be exploited to install adware on your device.
  5. Don't open links from suspicious sources. Email, SMS or messages to social.
  6. Use reliable security software and make sure it is always up to date and that PUA (Potentially Unwanted Applications) detection is enabled.

If you think your device is already infected with adware:

  • Disconnect your device from Wi-Fi and mobile data.
  • Restart it in safe mode (the process varies from device to device).
  • Go to Settings > Apps & notifications > See all apps and uninstall anything that looks suspicious.
  • Clear your browser's cache and cookies, if necessary.

“Alternatively, run a scan with reputable mobile security software,” advises Phil Muncaster from ESET. “As long as you follow the recommendation to enable PUA detections, you will be significantly helped in avoiding adware.”


Google preferences

Leave a Comment

Your email address will not be published. Required fields are marked *

Your message will not be published if:
1. Contains insulting, defamatory, racist, offensive or inappropriate comments.
2. Causes harm to minors.
3. It interferes with the privacy and individual and social rights of other users.
4. Advertises products or services or websites.
5. Contains personal information (address, phone, etc.).