- The attackers exploited a function of Discord which allows the reuse of expired or deleted invitation links, allowing them to compromise trusted community links and redirect users to malicious servers.
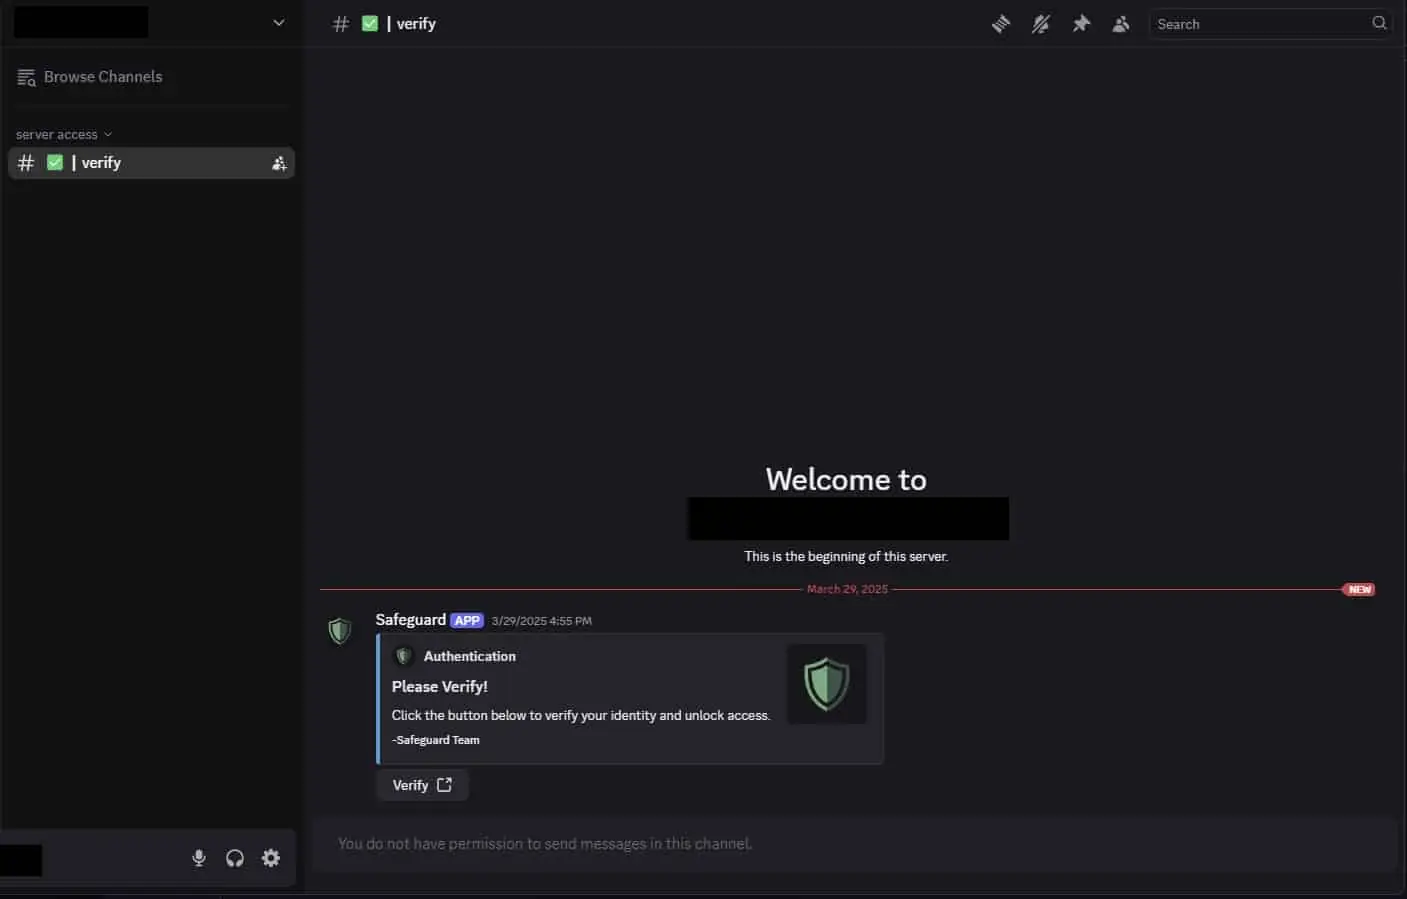
- The attack tricks users with a fake muzzle verification and a phishing website (Phishing) that look like legitimate servers Discord, leading victims to unknowingly execute harmful commands that download malware onto their computer.
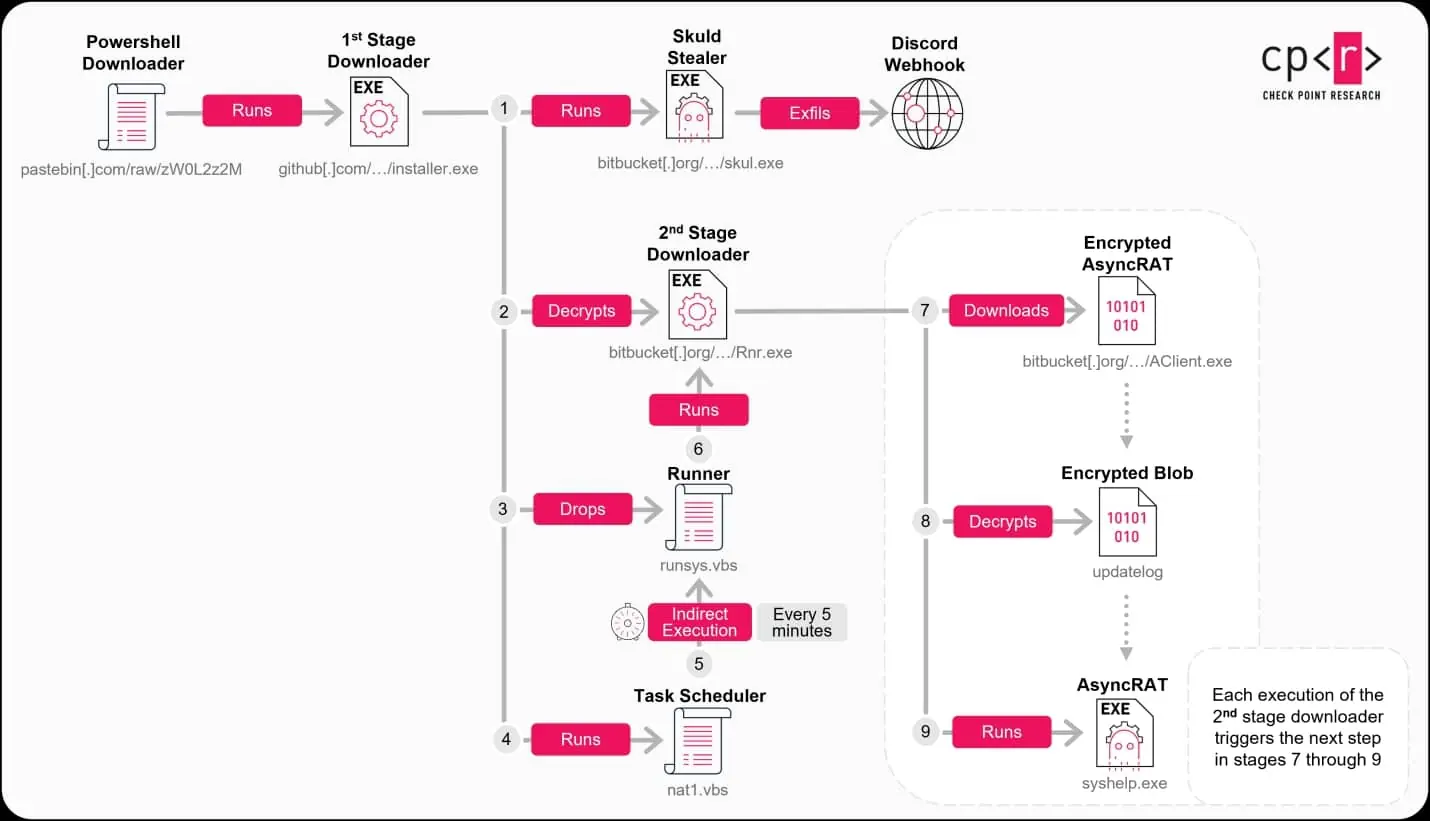
- Malware spreads silently in multiple steps using popular, trusted services like GitHub and its Pastebin to hide his activity and avoid detection.
- The attackers mainly target cryptocurrency users and aim to make money by stealing credentials and wallet information from victims around the world. Over 1.300 downloads were tracked, with victims spanning multiple countries, including the US, Vietnam, France, Germany, the UK and others, highlighting the global scale and financial motivation behind the campaign.

Introduction
Discord is a widely used and trusted platform preferred by gamers, communities, businesses, and others who need to connect securely and quickly. In a recent investigation , Check Point Research ( CPR ) uncovered a flaw in Discord ’s invitation system that allows attackers to hijack expired or deleted invitation links and secretly redirect unsuspecting users to malicious servers. Invitation links posted by trusted communities months ago on forums, social media, or official websites could now silently lead users into the hands of cybercriminals.
Check Point Research ( CPR ) observed real-world attacks in which threat actors leveraged compromised links to deploy sophisticated phishing schemes and malware campaigns. These included multi-stage infections that evaded detection by antivirus tools and sandbox checks , ultimately delivering malware such as AsyncRAT and Skuld Stealer . Below is a detailed analysis of the attack and practical advice to protect the public from such attacks.