Facebook new security loophole allows leaks

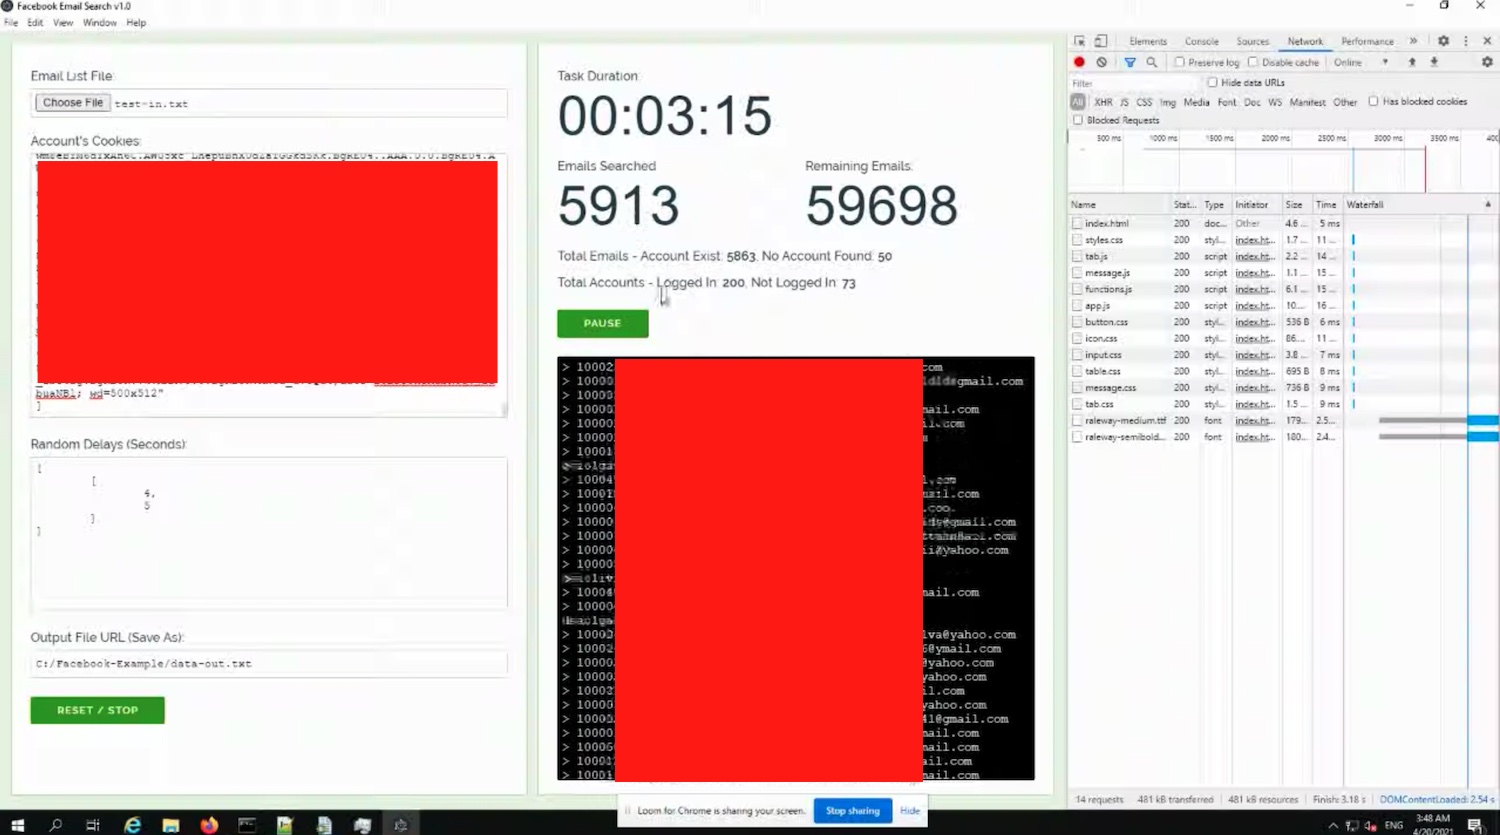
Hackers use a software called Facebook Email Search v1.0 to reveal millions of Facebook user email addresses, even if the addresses are private.

This user data, combined with the 553 million phone numbers leaked from Facebook a few weeks ago , could help hackers break into accounts or create a database of Facebook users' personal information.

See more articles from iGuRu.gr when you search for news on Google.

Facebook Email Search v1.0 uses a front-end vulnerability on the Facebook site. It automatically connects user IDs to the relevant email address, allowing a single hacker to secure about 5 million email addresses a day. Facebook says it fixed an almost identical vulnerability earlier this year.

In an interview with Ars Technica, an anonymous researcher claims that he sent the vulnerability to Facebook, but the largest social network chose to ignore the issue. Facebook told the researcher that it "does not consider [the vulnerability] to be significant enough to be fixed", despite the fact that it poses a clear security risk and breaches of its users' privacy.

Facebook not only ignored the vulnerability, but actively encouraged PR reps to downplay and “normalize” data breaches. Read an internal Facebook email accidentally sent to a Data News reporter after the April 5 leak.

Hundreds of millions of Facebook users saw their data travel online this month due to two separate social network vulnerabilities. In the face of this significant amount of data, Facebook hopes to "normalize" the phenomenon and argues that we should learn to live with data leaks. For a site that is obsessed with collecting data from its users, Facebook negligence causes.

Facebook now states that it "accidentally closed this bug report before launching it to the appropriate group" and that it is currently investigating the issue. We do not know when the company will fix this security gap or how many accounts have been affected.


Google preferences

Leave a Comment

Your email address will not be published. Required fields are marked *

Your message will not be published if:
1. Contains insulting, defamatory, racist, offensive or inappropriate comments.
2. Causes harm to minors.
3. It interferes with the privacy and individual and social rights of other users.
4. Advertises products or services or websites.
5. Contains personal information (address, phone, etc.).