The ransom message is just the beginning

ΤIn March 2024, a group that had carried out an attack on behalf of the gang ransomware BlackCat posted complaint on a cybercrime forum. The group had carried out the attack against Change Healthcare, one of the largest health data breaches in US history, but never received its fair share of the $22 million paid as ransomThe administrators of BlackCat allegedly kept the money and disappeared, posting a fake notice of FBI on their website to cover their departure.
The Change Healthcare case shows something that many companies still underestimate: ransomware is not an isolated attack by a hacker demanding money. It is an organized business model.

See more articles from iGuRu.gr when you search for news on Google.

Today, different groups take on different roles. Some gain initial access to corporate networks and resell it. Others develop ransomware tools . Affiliates carry out the attacks. Negotiators take on the communication with victims, while other networks help transfer and launder money.

By the time an organization sees the ransom message, the attack has already gone through many stages and many different players.

The ransom message is not the beginning of the attack. It is its final stage.

Too cheap to fail

If a company or organization treats a ransomware incident as a random intrusion that came out of nowhere, it’s likely that their defenses are designed with that in mind. However, such an approach may overlook how well-organized, well-armed, and repeatable the threat is.

The industry is structured so that each participant only needs to be competent in their own, limited function. The developer who maintains the ransomware platform and “brand” never needs to come into contact with the victim to make a profit. The partner pays a percentage or fee to gain access, using credentials that they did not collect themselves. The initial access broker, who sells access to a corporate network, does not know (nor does he need to know) what the buyer intends to do with those credentials.

But together, they have applied the logic of franchising to the ancient art of extortion, sharing the burden of responsibility along the way. And whenever an industry is organized in this way, massive expansion follows.

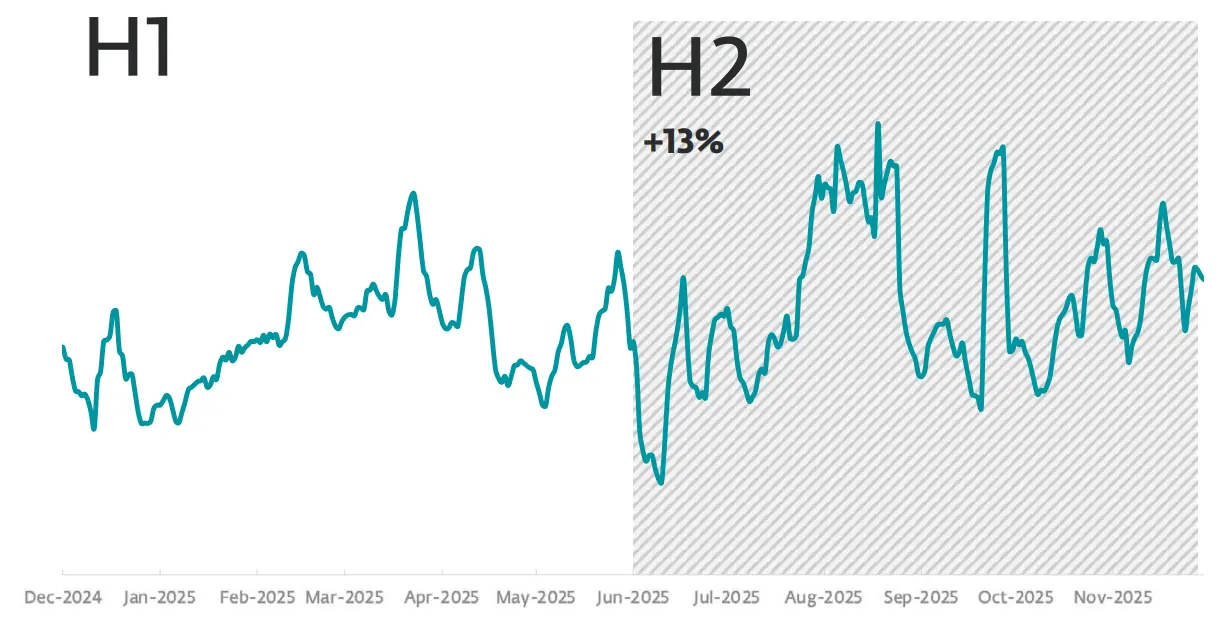
ESET data shows a 13% increase in ransomware attacks in the second half of 2025 compared to the previous year, following a 30% increase in the first half of the same year. Meanwhile, Verizon’s 2025 Data Breach Investigations Report (DBIR) saw a 32% to 44% increase in the rate of ransomware-related breaches, while the average ransom payment fell from $150.000 to $115.000. Targets are also shifting: Mandiant analysis shows a shift toward smaller companies with less mature defenses.

More (and easier) targets, combined with smaller profits, constitute a classic volume growth strategy.

Figure 1. Evolution of ransomware detection in the first half of 2025 and the second half of 2025, seven-day moving average (Source: ESET Threat Report H 2 2025 )

Ransomware is not " randomware " at all

Ransomware operations are designed to scale, regardless of whether each individual contributor has exceptional skills. In fact, the inner workings of what is often called ransomware-as-a-service (RaaS) are more complex than, say, a fast food chain: coordination is loose, and the struggles for dominance are real and, at times, public.

However, the underlying logic remains the same. The ransomware “industry” lives and dies on the trust between its members and the motivations that bind them together. It is known that motivations determine outcomes more than anything else.

Law enforcement is not sitting idly by. However, shutting down a company in a competitive market does not mean shutting down the market itself. As long as the incentives remain the same, the collapse of one ransomware group intensifies competition among the rest to fill the gap.

Because here too, competition works like in any market.

For example, when the LockBit and BlackCat groups were dismantled by law enforcement in 2024, their collaborators largely moved to the RansomHub group. In 2025, DragonForce – a relatively small player until then – defaced the websites of several competitors and took down the RansomHub group’s platform, which was the dominant force at the time. After RansomHub was shut down, the Akira and Qilin groups absorbed a significant portion of its market share.

This pattern persists because barriers to entry remain low: tools are available as a service, while “labor” is so expendable that the supply is inexhaustible.

The Red Queen's Race"

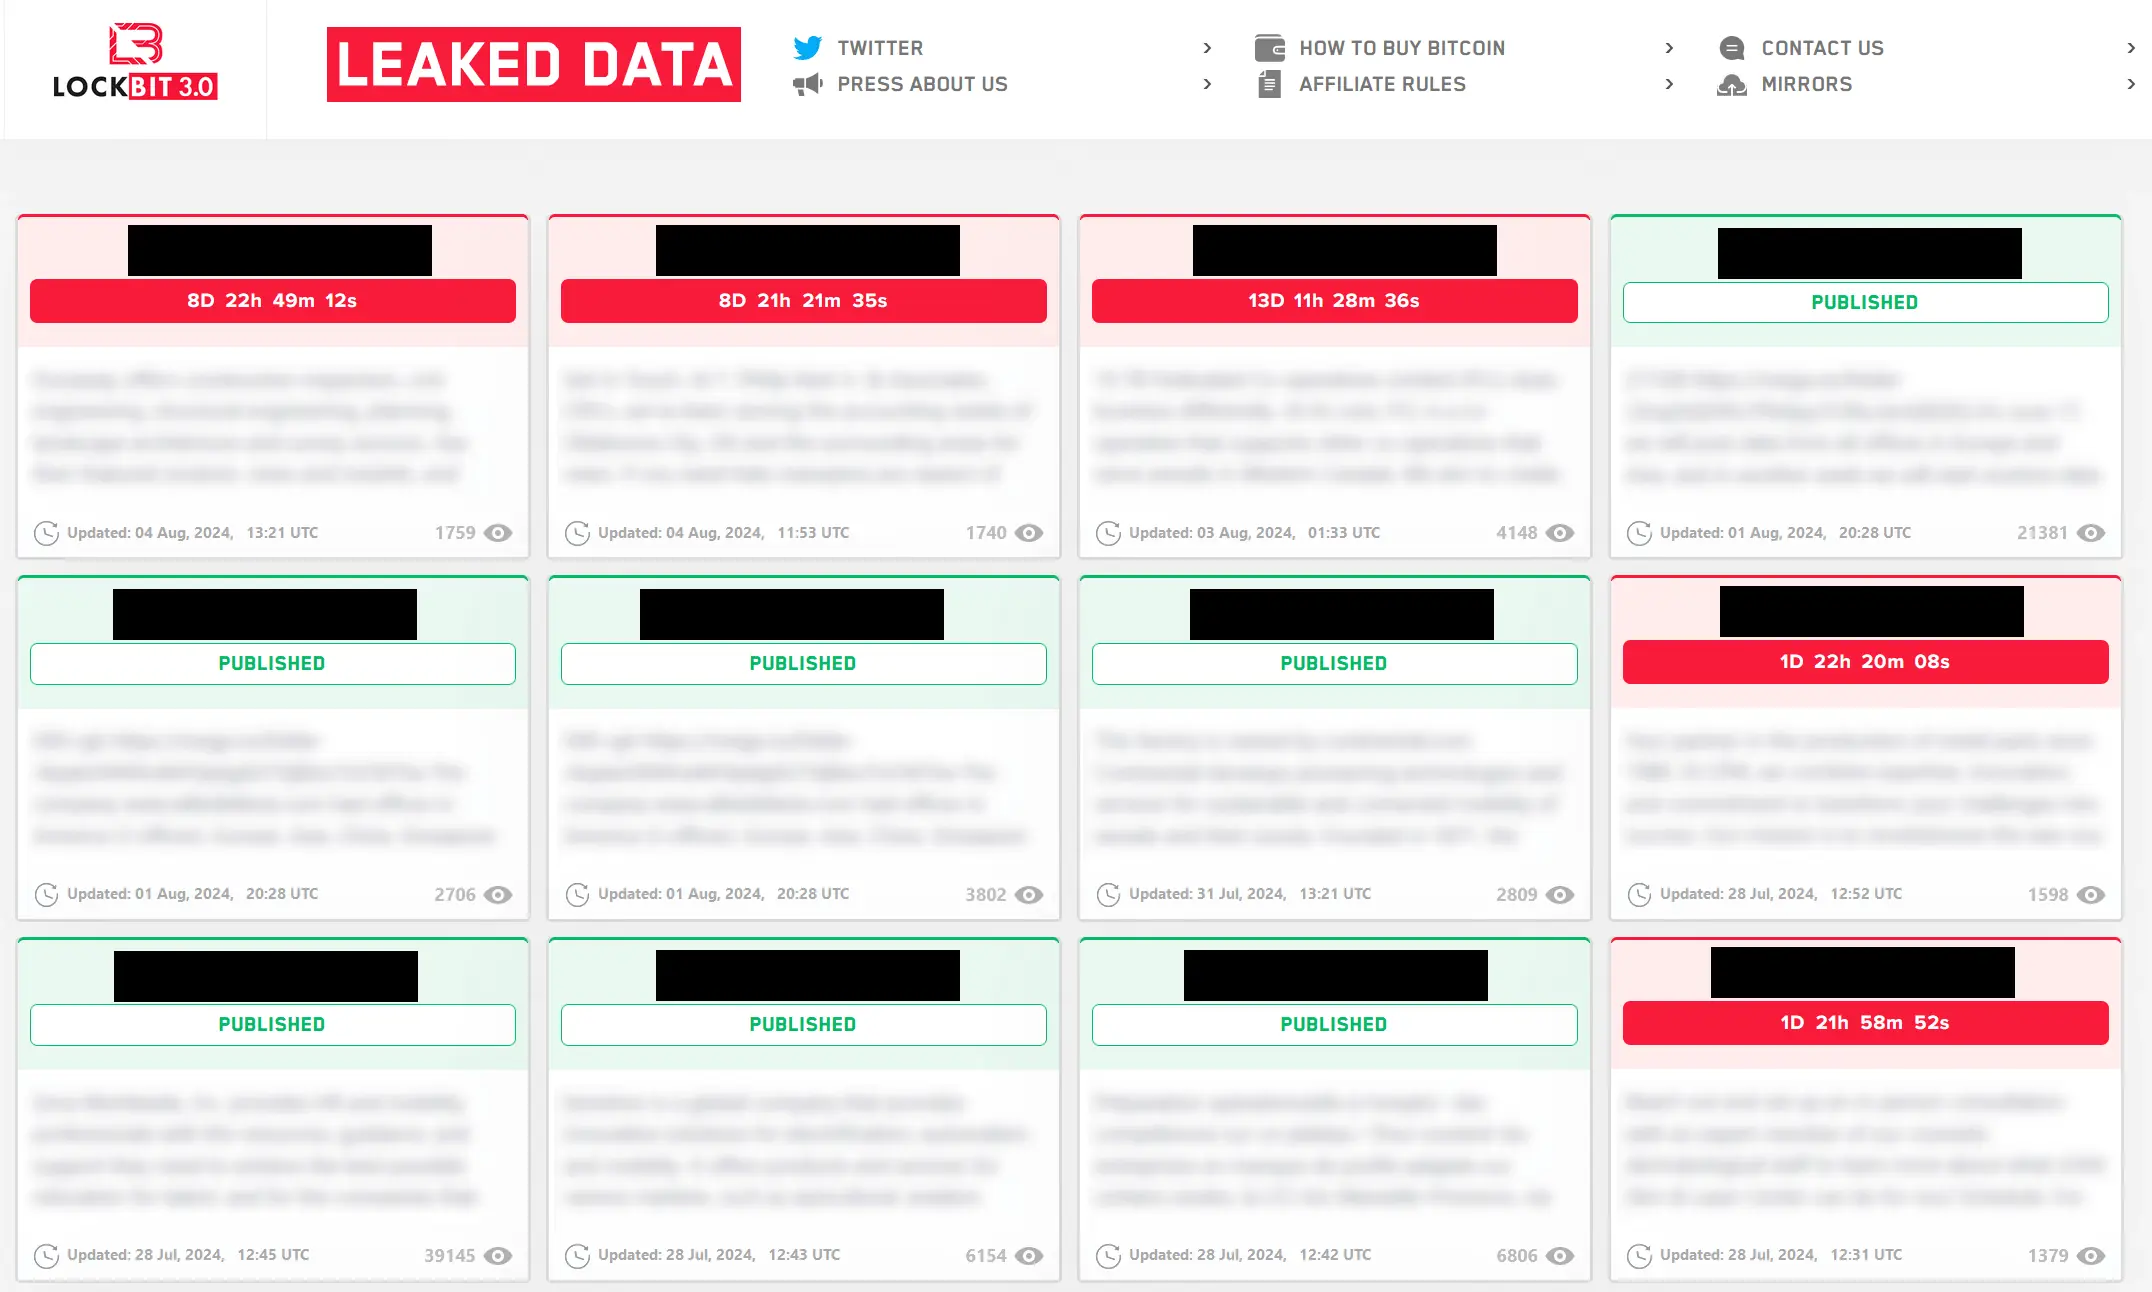
Cybercrime never stands still. The traditional ransomware tactic – locking files and demanding a ransom – has now evolved into a two-pronged attack. In this model, attackers first steal corporate data and then encrypt it, posting samples of their loot on specialized leak websites. The FBI and CISA now routinely describe ransomware as a “data theft and extortion” problem.

Figure 2. LockBit leak website (Source: ESET Research )

But the specific risks are changing rapidly. Just two years ago, ClickFix – a social engineering technique in which a fake error message tricks users into copying, pasting, and executing malicious commands – was virtually unknown. Today, it has become widespread and is used by both state-sponsored groups and cybercriminals.

On the other hand, the speed of adaptation is not surprising, considering that a similar dynamic is observed in nature. Species that compete with each other must constantly adapt simply to maintain their position. Predators become faster, and prey follow. Prey develop camouflage, and predators acquire sharper vision. Biology describes this phenomenon as the “Red Queen effect,” after the character in Lewis Carroll’s book “Through the Looking Glass,” who must constantly evolve (run) just to stay in the same place.

Security professionals readily recognize this dynamic, although the more familiar terms – such as “arms race” or “cat and mouse game” – do not fully capture it. “Red Queen” describes something more specific: a constant evolution that does not yield a clear advantage, since the opposing side is also evolving almost simultaneously.

The most prominent manifestation of this dynamic is in the space between defense tools and attack tools. Endpoint detection and response (EDR) products, as well as extended detection and response (XDR) systems, are key tools for detecting ransomware partner activity on compromised networks. As these tools improve, cybercriminals are responding by developing an underground market of tools specifically designed to bypass or disable them.

And where there is demand, there is supply, usually in abundance.

ESET researchers have identified nearly 90 “EDR killers” in active use. Fifty-four of these malicious tools leverage the same basic technique: they load a legitimate but vulnerable driver onto the target system and use it to gain kernel-level privileges, which are required to disable the security product.

This technique is called “Bring Your Own Vulnerable Driver” (BYOVD). Vulnerable drivers act as a kind of “commodity”: the same driver appears in unrelated tools, while the same tool may use different drivers in separate campaigns.

The market for EDR killers reflects the economics of the ransomware they serve. These tools often come with subscription-based obfuscation services that are regularly updated to stay one step ahead of detection mechanisms. Typically, partners, not ransomware operators themselves, choose which “killer” to deploy, with the purchase decision being made at the franchise level. When the defense product is updated, so does the corresponding obfuscation service. The Red Queen, again.

The extensive investment in EDR killers is, in a way, the clearest measure of the effectiveness of detection tools against the criminal business model. After all, you don't create an entire product category to neutralize something that doesn't affect your bottom line.

These malicious tools are likely to spread even further as AI makes the market – and, more broadly, the cybercrime economy – more accessible. ESET researchers believe that AI has already contributed to the development of some EDR killers, with the Warlock gang’s products being a prime example.

At the same time, other researchers have documented the phenomenon they call "vibeware": malware that is mass-produced with the help of artificial intelligence and aims to flood the target environment with disposable code, increasing the likelihood that a version will go unnoticed.

The barrier to creating malware has been lowered to such an extent that the key limiting factor is now intent rather than specialized skills, a development that reflects broader trends in the cybercrime space.

Market analysis

If we view ransomware simply as an attack, we create defenses that are solely aimed at countering attacks. However, if we approach it as an entire industry, different and more complex priorities emerge.

How is the “Red Queen” dynamic evolving between defense products and attack tools? What malicious tools, techniques, and processes are currently in circulation? Can your security system fend off a BYOVD attack that leverages currently available drivers? What will happen to your environment if an MSP in your supply chain is compromised? Which ransomware actors are actively targeting your sector and which EDR killers are they using?

If you can’t answer these urgent questions, it’s likely that by the time the outcome of this “industry” reaches you, much of the attack chain will have already been executed. You can’t predict which group will attack, at what point in time, or via what route. But you can keep an up-to-date map of where active groups are headed and assess whether any of those routes could lead to your door.


Google preferences

Leave a Comment

Your email address will not be published. Required fields are marked *

Your message will not be published if:
1. Contains insulting, defamatory, racist, offensive or inappropriate comments.
2. Causes harm to minors.
3. It interferes with the privacy and individual and social rights of other users.
4. Advertises products or services or websites.
5. Contains personal information (address, phone, etc.).