New research from Check Point Research (CPR) reveals that modern large language models (LLMs) can now transform general malicious ideas into practical cyberattack scenarios, significantly reducing the technical level required to create new attacks.
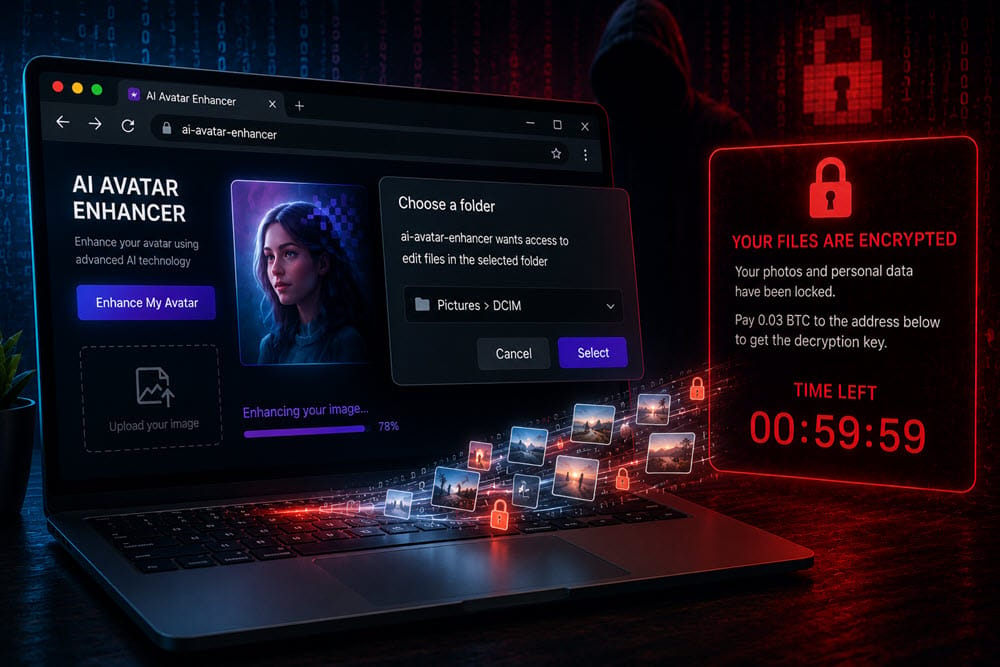
At the heart of the research is a new technique that researchers call Web Browser Only RansomwareThe attack is carried out exclusively through the browser, without the installation of an application, malware (APK), exploit or root privileges. Instead, it is based solely on social engineering and the abuse of legitimate functionality. File System Access API, which allows websites to access files after user approval.
The research shows that an attacker could present a seemingly innocent AI service – such as a photo enhancement app – asking the user for access to their images folder. With a single authorization, the website could gain the ability to read, modify or even encrypt the user’s files, without installing any software on the device.