ESET Research Center has detected a new variant of the NGate malware family that, instead of the previously used NFCGate tool, exploits a legitimate Android application called HandyPay. The attackers modified the NFC data transfer application, incorporating malicious code that appears to have been generated using artificial intelligence.
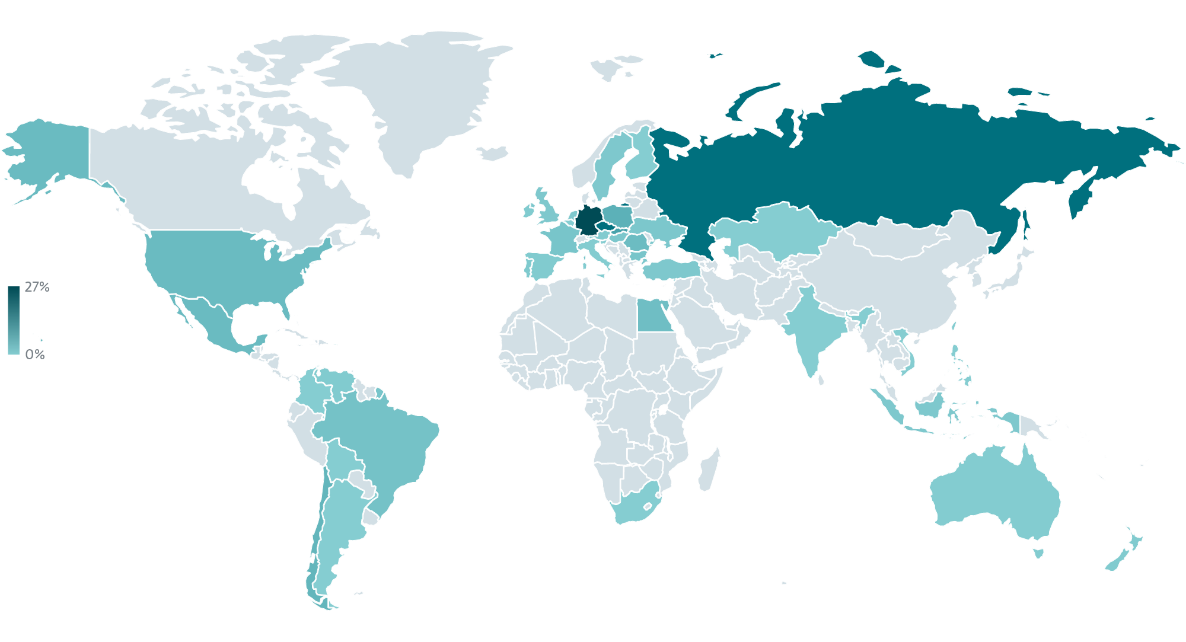
As with previous versions of NGate, the malware allows attackers to transfer NFC data from a victim’s payment card to their own device and use it for contactless ATM cash withdrawals and unauthorized payments. It can also capture victims’ payment card PINs and send them to the attackers’ command and control (C&C) server. The primary targets of this malware are located in Brazil. However, NFC-based attacks appear to be expanding to other regions.