The Louvre's video surveillance password was "LOUVRE"

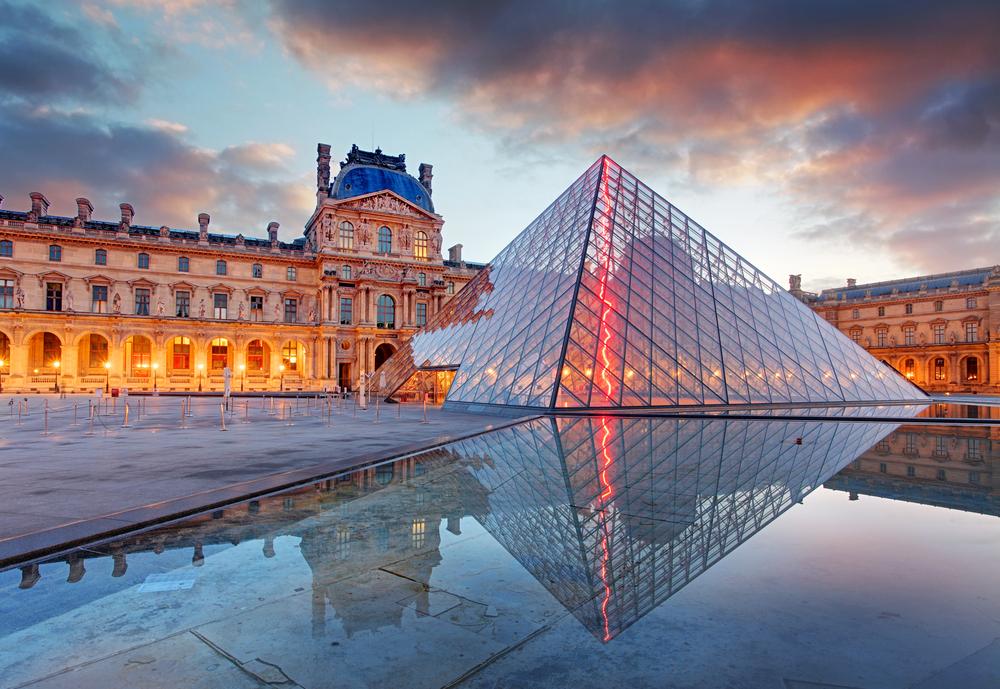
An Oct. 18 robbery, in which $102 million worth of crown jewels were stolen from the Louvre in broad daylight, exposed years of lax security at the national art museum.

With weak passwords like “LOUVRE” to decades-old systems that are no longer supported and easy access from the rooftop, the job was done very easily.
See more articles from iGuRu.gr when you search for news on Google.

The Louvre used the password “Louvre” for its video surveillance servers. That’s no exaggeration. Confidential documents reviewed by Liberation detail a long history of security vulnerabilities at the Louvre, dating back to a 2014 cybersecurity audit conducted by the French Cybersecurity Agency (ANSSI) at the museum’s request. ANSSI experts managed to penetrate the Louvre’s security network, gain access to video surveillance, and modify access.

How did the experts manage to penetrate the network? Mainly because of the weakness of some passwords, which the French National Cybersecurity Agency (ANSSI) politely describes as “trivial,” writes Brice Le Borgne of Liberation.

“Type 'LOUVRE' to access a server that manages the museum's video surveillance, or 'THALES' to access one of the software programs published by Thales.”

The museum requested another audit from France’s National Institute for Advanced Studies in Security and Justice in 2015. Two years later, the audit’s 40 pages of recommendations described “serious deficiencies,” “mismanagement” of visitor flow, roofs that are easily accessible during construction work, and outdated and dysfunctional security systems.

Later documents show that in 2025, the museum was still using security software purchased in 2003 and no longer supported by its developer, which was running on hardware using Windows Server 2003.


Google preferences

Leave a Comment

Your email address will not be published. Required fields are marked *

Your message will not be published if:
1. Contains insulting, defamatory, racist, offensive or inappropriate comments.
2. Causes harm to minors.
3. It interferes with the privacy and individual and social rights of other users.
4. Advertises products or services or websites.
5. Contains personal information (address, phone, etc.).