Fake emails with voicemail transcriptions

Automated voicemail transcripts have become a part of everyday corporate communication. They arrive with familiar subject lines, system-generated formatting, and minimal additional information. These very characteristics make them easy to be perceived as trustworthy and go unnoticed. Attackers are now capitalizing on this familiarity, turning ordinary call transcript notifications into phishing vehicles for stealing credentials.

Check Point researchers have uncovered a widespread phishing campaign that is taking advantage of this shift in business habits. The emails mimic automated voicemail transcription alerts and contain malicious SVG vector graphic file attachments. The files redirect users to credential-sniffing pages, turning a familiar collaboration process into a potential conduit for account compromise.

See more articles from iGuRu.gr when you search for news on Google.

Phishing campaign designed to look ordinary

From August 17 to August 31 , Check Point detected more than 58.000 emails associated with the campaign. The operation targeted over 7.800 organizations, using more than 38.400 spoofed sender addresses on more than 9.300 spoofed domains.

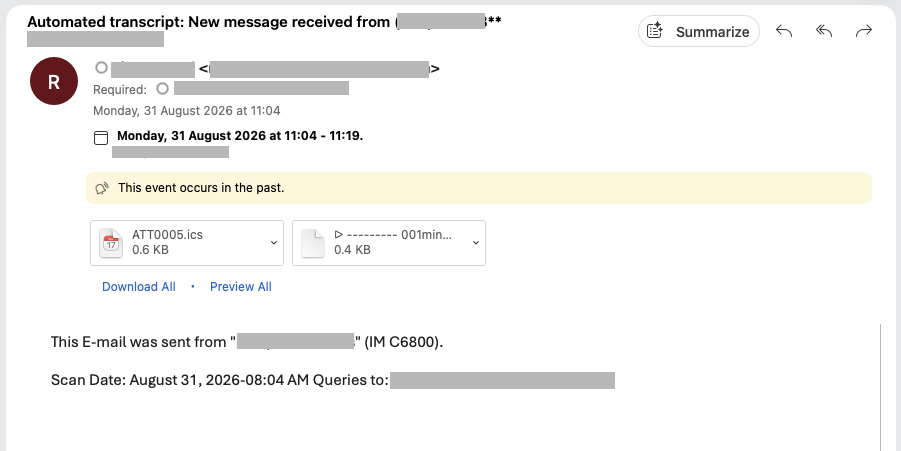
The subject lines follow a simple formula. Each one begins with the phrase “Automated transcript” and continues with a partially masked phone number and a random tracking code. The message is intentionally discreet, resembling an alert generated by a trusted corporate system.email phishing campaign

The chain of attack

The campaign relies heavily on trust-inspiring cues that are difficult for users to quickly assess. Each email displays the recipient's own domain as the sender, making the message look like an internal system notification before the attachment is even opened.

The attachment is designed to look like a call log file, with names like “▷ ——— 001min 09sec_….svg.” In reality, it is an SVG file that contains an embedded script. When opened, the script redirects the user to a phishing page. Because the user’s email address is already encoded in the URL, the fake login form can auto-fill it, making the credential-snatching process more personalized and convincing.

Basic features

  • Sender addresses are forged to match the recipient's domain and make the message appear internal.
  • Subject lines mimic notifications that real voicemail and call transcription systems produce.
  • The malicious payload is delivered as an SVG file rather than a traditional executable file or macro-enabled document.
  • The redirection is performed on the user's device, with no visible link that could be checked before opening the attachment.
  • The landing page already has the victim's email address pre-populated, reducing the steps required and making the fake login form more convincing.

How Check Point Email Security stops the attack

The campaign highlights the limitations of defense mechanisms that rely primarily on reputation scores, known malicious links, or obviously dangerous attachment types. The sender is spoofed, the bait looks familiar, the malicious payload is in an SVG file instead of a traditional executable, and the user is only taken to the malicious destination after opening the file.

Check Point Email Security is designed to stop these threats before they reach your inbox. Powered by ThreatCloud AI and more than 60 AI engines, it analyzes sender behavior, message context, attachment characteristics, the nature and destination of URLs, and phishing signals throughout the attack chain. This multi-layered analysis is critical when attackers use changing infrastructure, redirects that run on the user’s device, and file types that appear harmless to conventional filters.

In campaigns of this type, Check Point Email Security evaluates the spoofed sender domain, the automated transcription pretext, the suspicious SVG attachment, the behavior of the embedded redirect, and the credential-sniffing page. By correlating these clues, it can prevent message delivery, quarantine malicious attachments, and block access to phishing websites if the attack continues through the browser.

The broader risk of automated trust

This campaign shows how quickly attackers are adapting to corporate workflows as automation expands. AI agents are increasingly taking on the role of sorting incoming emails, summarizing messages, processing attachments, and initiating next actions on behalf of users. As this responsibility expands, the same social engineering techniques that affect employees can pose risks to automated workflows if proper controls are not in place.

For example, an AI agent or automated workflow that has permission to open attachments or follow links could process a file called “call recording” without the judgment that a security-aware user would expect. This scenario highlights the need for corporate controls, access restrictions, and monitoring of automated systems that handle incoming content.

How can organizations mitigate risk?

  • Treat "automated" notifications as a reason for verification and not as a reason to relax controls, especially when the sender appears to be using your own domain.
  • Before allowing an AI agent to open attachments, follow links, or act on incoming content, determine which file types and domains it can access without human confirmation.
  • Check SVG attachments as active content, not just images.
  • Record and monitor the actions of AI agents as you would monitor the activity of users with privileged access, so that potential malicious use or violation is identified in a timely manner.
  • Encourage users to report suspicious automated emails so security teams can identify the underlying infrastructure and block subsequent attempts.


Google preferences

Leave a Comment

Your email address will not be published. Required fields are marked *

Your message will not be published if:
1. Contains insulting, defamatory, racist, offensive or inappropriate comments.
2. Causes harm to minors.
3. It interferes with the privacy and individual and social rights of other users.
4. Advertises products or services or websites.
5. Contains personal information (address, phone, etc.).