Quishing : Phishing via QR code

In the world of cybersecurity, the biggest danger often lies behind something that seems completely familiar to us. When we see the same thing over and over again, we stop paying attention to it. We trust it almost mechanically.

Think about how many times a day we encounter a QR code: on a restaurant menu, on a light pole, on a parking meter. Now the little black and white codes are appearing more and more often in our email inboxes. And it's precisely this familiarity that can make them dangerous.quishing
See more articles from iGuRu.gr when you search for news on Google.

Because behind a QR can also be hidden a malicious link. A link that is not immediately visible, that can go unnoticed by traditional corporate security filters and, with a simple scan, transfer the interaction from the protected corporate computer to the employee's personal mobile phone, where controls may be less strict.

"Cybercriminals are constantly trying new ways to go unnoticed. One of these methods is 'quishing': attacks that use QR codes to lure unsuspecting employees into malicious actions," says Phil Muncaster at WeLiveSecurity, the information platform of global cybersecurity company ESET.

Here's what you need to know to help protect your organization.

Why is quishing so dangerous?

A QR code, short for “Quick Response,” is a two-dimensional barcode that can encode URLs, payment information, contact information, and other data. It helps users quickly get from point A to point B, where the destination, in this case, is usually a website or an app.

QR codes are attractive to threat actors for a number of reasons. Their widespread use, accelerated by the increased demand for contactless interactions during the pandemic, has made them an integral part of everyday life. As a result, we are much more likely to pull out our phones to scan a QR code today than we were a few years ago.

QR codes also fit seamlessly into phishing workflows: the malicious link or attachment is simply replaced by a QR code. What’s more, these codes can be generated in a matter of seconds. In fact, many phishing tools have a dedicated QR code generator. Most importantly, however, they take the victim from a relatively well-protected corporate environment to a potentially unmanaged mobile device, thereby bypassing some of the corporate-level security controls.

A major advantage for the attacker is the ability to hide. The destination is encoded in a visual pattern and is not displayed as readable text. This hides the malicious URLs and prevents some traditional email filters from extracting and checking them. Sometimes, the hiding is made even more effective as QR codes are embedded in PDF or JPEG attachments. This makes them more likely to end up in employees’ inboxes.

When such a message arrives in the inbox, staff can have difficulty distinguishing a genuine message from a malicious one. There is usually not enough text to check for spelling or grammatical errors, while the link is essentially hidden within a visual pattern and therefore invisible to the human eye.

When used in conjunction with a trusted brand , for example, in an email that appears to come from DocuSign or an update from Microsoft, a quishing attack leverages similar social engineering tactics to classic phishing emails.

The trusted brand identity reassures the victim that they can scan the code and continue without risk. Meanwhile, malicious QR codes are often embedded in notifications that urge users to protect their account or perform an authentication check to verify their details.

In fact, according to ESET's H1 2026 Threat Report , malicious QR codes were embedded in at least 11% of all phishing emails in the first half of 2026.

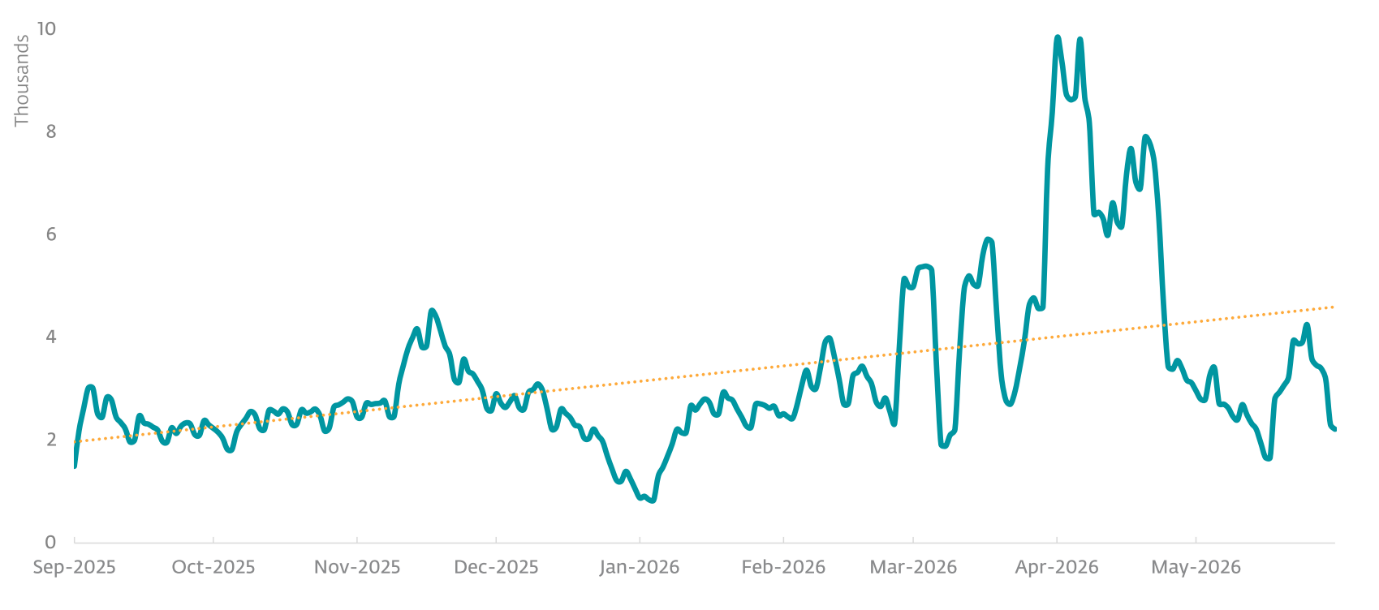
“ESET monitors quishing emails under the name QRCode/Phishing detection. This detection operates through a special layer of ESET’s email scanner, designed to detect QR codes in the vast majority of file types and decode the URLs they contain. The extracted URLs are scanned through ESET’s anti-phishing, anti-malware, and anti-spam engines. Any malicious URLs are blocked and the corresponding emails are flagged or deleted,” the report states.

es
Trends in detection QRCode/Phishing from September 2025 to May 2026, seven-day moving average (source: Threat Report ESET, 1st half of 2026)

Threat actors continue to innovate

As with any trend in the threat landscape, malicious actors continue to refine their techniques for maximum impact.

Quishing attacks are used not only to install malware and steal credentials, but also to steal MFA tokens. Security researchers have also identified their use in attacks designed to:

  • Bypassing security measures the app store via direct app downloads, where malware masquerades as a legitimate app
  • Instead of leading the user to a malicious website or phishing website, the link takes you directly to a legitimate social networking, payment, or other application. This can be used in a variety of scenarios, such as:
  1. Account takeover, where the victim is directed to authenticate the attacker to their account
  2. Financial fraud, where the victim is directed to a payment application with the beneficiary details filled in
  3. Contacts or calendar infection, where malicious meeting links or new contact details are embedded in utility apps and redirect users to phishing websites.
  • Obfuscation of security tools by converting long, malicious internet addresses into short links, which are then embedded in QR codes.

es1


Example of a phishing email detected by ESET products as QRCode/Phishing (source: ESET Threat Report H1 2026 )

Even state-sponsored APT groups use “quishing.” In January 2026, the FBI reported that the Kimsuky group, which is linked to North Korea, was targeting think tanks, academic institutions, and government agencies in the U.S. and other countries using QR codes embedded in spearphishing emails. The bait varied. In some cases, the emails claimed that scanning the code would lead users to questionnaires, registration landing pages, or secure storage drives.

How to protect your business from QR phishing

Fortunately, a well-designed combination of changes in people, processes and technology can help significantly reduce the risk of quishing.

Start with people. Incorporate anti-quishing into user awareness training programs and simulation exercises. Encourage employees to avoid scanning QR codes in unsolicited emails and to report anything suspicious. If they believe it comes from a trusted source, they should contact the sender, using contact information obtained from a source other than the message.

Then, consider implementing technical controls , including email security, to minimize the risk of “quishing” emails ending up in users’ inboxes. Add a mobile security solution to employee devices to block access to malicious websites. Also, require the use of phishing-resistant multi-factor authentication (MFA) on all sensitive accounts, so that even if users are tricked, attackers cannot gain access to corporate systems. Mobile device management (MDM) tools can help you ensure that all devices are protected according to corporate policy.

Reduce the attack surface , enforce the principle of least privilege and just-in-time access. Keep all mobile operating systems and corporate software up to date, including security tools. Also, constantly monitor for suspicious activity. Practice implementing incident response plans in case the worst-case scenario occurs.

It's no longer a novelty

QR codes have gone from being a novelty to a common occurrence in the business world. The same is true for “quishing.” Familiarity shouldn’t lead to complacency. Just as staff have become accustomed to treating traditional email and SMS phishing with suspicion, they can be trained to recognize the warning signs of a potential “quishing” attempt, notes Muncaster of ESET’s WeLiveSecurity. Under the right circumstances, familiarity can enhance security.


Google preferences

Leave a Comment

Your email address will not be published. Required fields are marked *

Your message will not be published if:
1. Contains insulting, defamatory, racist, offensive or inappropriate comments.
2. Causes harm to minors.
3. It interferes with the privacy and individual and social rights of other users.
4. Advertises products or services or websites.
5. Contains personal information (address, phone, etc.).