What happens when your personal data goes to the Dark Web?

Forget everything you think you know about the dark web. It's not just a digital den of criminals, as some commentators often describe it.

Beneath the surface of the encrypted internet lies a parallel world: many legitimate sites and forums that offer privacy-enhanced content and services, helping individuals and communities evade censorship and oppression. For them, anonymity is survival.

See more articles from iGuRu.gr when you search for news on Google.

But, the truth is that the dark web also attracts cybercriminals like a magnet, who visit forums, illegal markets and sites without worrying that someone is following their tracks or revealing who they are, explains Phil Muncaster from the team at digital security company ESET.

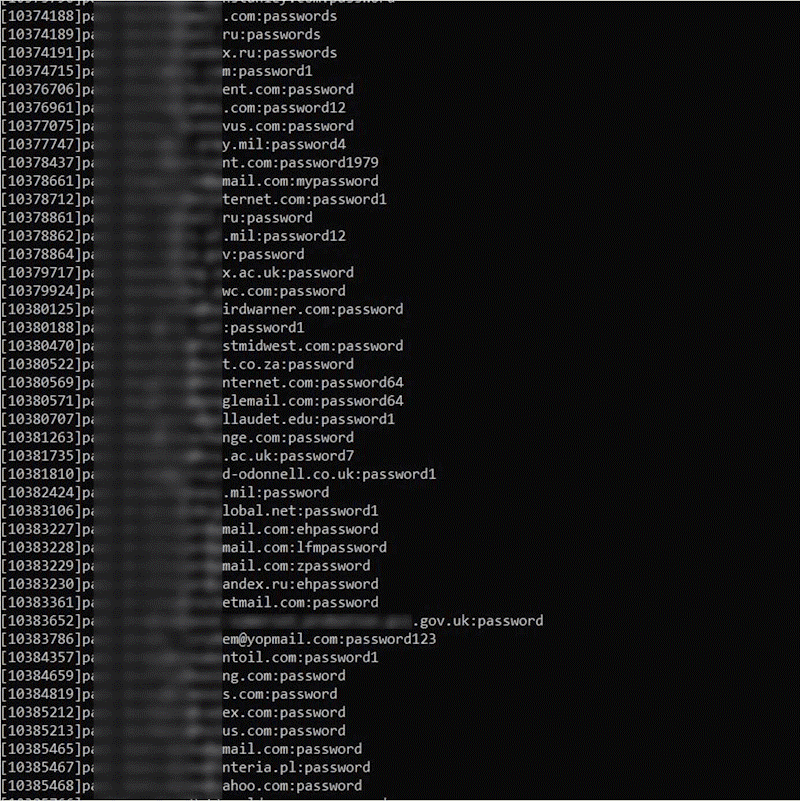
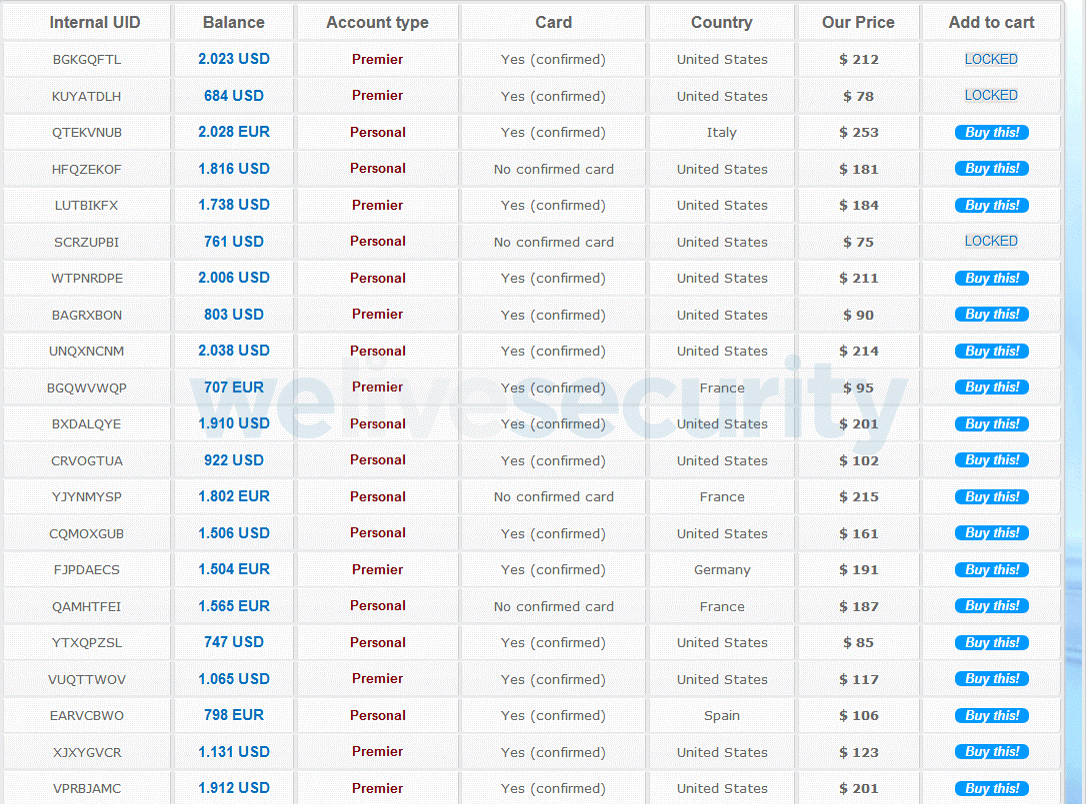
Many of these platforms exist solely to facilitate the trade of stolen personal and financial information. Here, your personal data is often bought and sold alongside other items, such as drugs, hacking tools, and exploits.

The question, then, is clear: what will you do if you discover that your data is being sold on one of these websites?

But first, let's look at how personal data ends up on the dark web and what cybercriminals really want.

How personal data ends up on the dark web

There are several ways in which financial data , Personally Identifiable Information ( PII ) , and credentials can fall into the hands of cybercriminals.

  • Data breaches include the theft, on a large scale, of customer or employee information, which is then typically listed for sale on the dark web. The United States was on track to set a new record in this area, having already recorded 1.732 incidents in the first half of 2025, resulting in more than 165,7 million data breach notifications. As we all now interact with an increasing number of companies online, the risk of being involved in a breach is constantly increasing. Most of us will have received at least one relevant email notification. This risk is further exacerbated by the spread of double-extortion ransomware attacks, where data is stolen with the aim of not only encrypting it, but also blackmailing the victim company by threatening to leak it.
  • The Infostealer malware (or spyware) does exactly what its name suggests. It has become extremely popular thanks to “as-a-service” kits such as RedLine and Lumma Stealer. The malware can hide in seemingly legitimate mobile apps, websites, malicious ads, and phishing links or attachments. The data collected is then aggregated by the perpetrators and sold on the dark web. Not only login credentials are often stolen, but also session cookies, making it easy for hackers to bypass even multi-factor authentication (MFA).
  • Electronic fishing (Phishing) has long been one of the most common ways to steal information from unsuspecting victims. However, the emergence of genetic artificial intelligence (GenAI) tools has made it much easier for threat actors to scale their attacks, personalize them, and craft them in flawless language, thus increasing the chances of success. If a user unknowingly clicks and enters their details on a phishing page, that information can be sold on the dark web.
  • Accidental data leaks are also common on the internet. They are often caused by misconfigurations of cloud systems, such as not requiring a password to access online databases. This can leave sensitive data exposed to anyone who knows where to look or has scanned the internet for such vulnerabilities. If a database is left open for a long time, it is at risk of being stolen and sold on the dark web. In some cases, threat actors may even delete the original database in order to blackmail the victim business.
  • Supply chain attacks are similar to classic data breaches, except that instead of directly compromising the company with which the user shared their data, the target is a vendor or partner organization. These third parties are legally permitted to access and use the information, but they often do not have the same level of robust security. This makes them attractive targets, as a single successful attack can provide access to data for many corporate customers. In many cases, these vendors are digital service providers. A prime example is Progress Software, which exploited a zero-day vulnerability in its popular file transfer software MOVEit in 2023, affecting thousands of organizations and more than 90 million customers. Another potential weak link is data brokers, who collect information legally through web scraping and monitoring mechanisms, but do not always adequately protect it.

Figure 2. PayPal and credit card accounts for sale, as identified by ESET researchers.

What do they want?

What cybercriminals are really after is access to financial data, such as bank account numbers, credit card details and login credentials, as well as personally identifiable information (PII) and account access details. With this information, they can take over accounts, extract data and money, and potentially access stored card details. They can also use PII in subsequent phishing attempts to further steal financial information.

Alternatively, PII can be used for identity fraud, such as applying for new lines of credit, obtaining medical care, or claiming social benefits in the victim's name.

Biometric data is considered particularly sensitive, as it cannot be “reissued” or replaced like a password. Similarly, session tokens and cookies are extremely valuable to threat actors, as they can allow them to bypass multi-factor authentication (MFA) mechanisms.

The financial impact of such attacks can be particularly severe. According to a recent report by the Identity Theft Resource Center (ITRC), 20% of fraud victims in the US reported losses of more than $100.000 in a single year, while more than 10% reported losses of at least $1 million.

What to do if you find your information on the dark web

If you receive a notification that your personal and/or financial information has appeared on the dark web, it is important to act immediately, explains Phil Muncaster from the ESET team. Depending on the type of data that has been leaked, the following measures are recommended:

  • Change all compromised passwords immediately. Make sure you use strong and unique passwords for each account and store them in a trusted password manager.
  • Enable multi-factor authentication (MFA) on all accounts. Prefer authenticator apps or physical security keys over SMS, which can be intercepted.
  • Log out of all devices. This prevents access by hackers who may have obtained session cookies.
  • Contact your bank immediately. Request that your cards be frozen and reissued if there is a risk of financial fraud.
  • Enable alerts for suspicious transactions and consider freezing your Teiresias account (or other similar service) to prevent your details from being used for new loans or credits.
  • Scan all your devices for malware. Special attention should be paid to software that steals credentials or personal data.
  • Report the leak to the appropriate authorities.

Long-term measures to protect your personal data

Once the situation calms down, there are specific steps you can take to reduce the risk of sensitive information ending up on the dark web. Consider using services like Hide My Email to limit the amount of personal data companies store. It's also good practice to complete your purchases as a guest and never save credit or debit card details when shopping on third-party websites.

Then, reduce your chances of getting infected by infostealers and phishing attacks by installing reliable security software on all your devices and computers. Only download apps from official stores and be especially careful with unsolicited emails, SMS or social media messages that contain links or attachments.

Additionally, limit the amount of data available to data brokers by ensuring that all your social media accounts are set to “private.” Use encrypted communication services, as well as browsers and search engines with enhanced privacy features. You can also consider submitting “right to be forgotten” requests to data brokers, possibly through specialized services with the necessary expertise.

Finally, sign up for identity protection services and websites like Have I Been Pwned , which alert you when personally identifiable information (PII) appears on the dark web. Having your personal information and login details compromised can be both emotionally taxing and financially damaging. Additionally, reusing login details for work accounts can have serious career implications if it allows hackers to gain access to corporate resources.


Google preferences

Leave a Comment

Your email address will not be published. Required fields are marked *

Your message will not be published if:
1. Contains insulting, defamatory, racist, offensive or inappropriate comments.
2. Causes harm to minors.
3. It interferes with the privacy and individual and social rights of other users.
4. Advertises products or services or websites.
5. Contains personal information (address, phone, etc.).