Piraeus Bank - Phishing: What You Need to Know

Piraeus Bank published a warning on its blog in order to protect its customers (and not only). Below we quote the post and we hope others will follow. The Greek public needs basic education in the use of the internet and in the security of transactions.

Piraeus Bank states :

See more articles from iGuRu.gr when you search for news on Google.

With fraud cases on the rise, security awareness is essential.

One of the topics presented in the last period is Phishing. The practice of Phishing (electronic data fishing) uses emails or sms as a means to intercept the person's personal data. These messages contain misleading content and their senders impersonate a legitimate organization/company/bank. They aim to extract confidential personal and financial data such as online banking usernames, passwords, debit/credit card details, etc. This data can then be used to make unauthorized financial transactions resulting in financial loss. The majority of Phishing messages claim either a problem with your account, or require your confirmation to execute a transaction, (which has not received an official order from you), or a service upgrade action, or confirmation of personal data.

1903x750px blog post 01

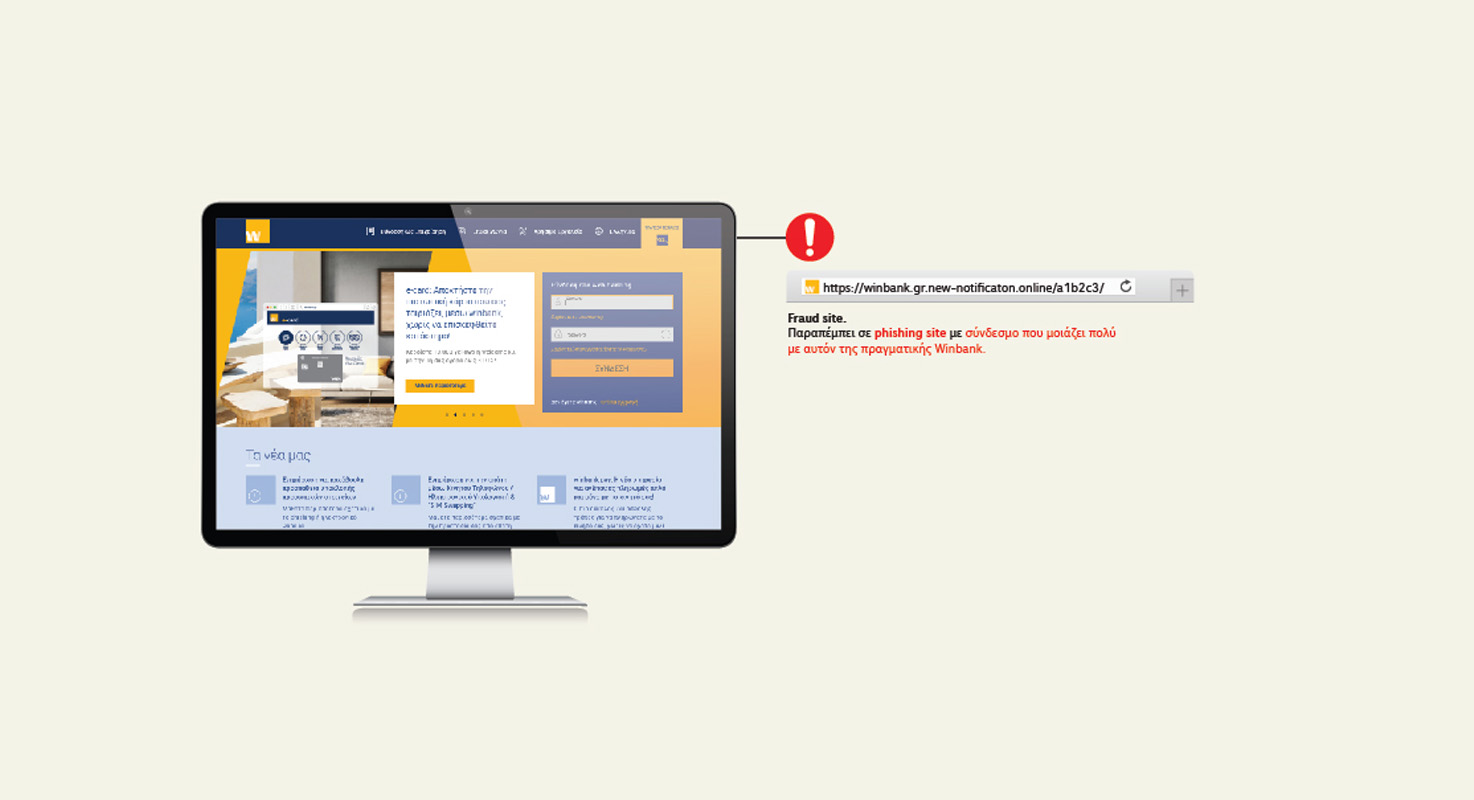
Regarding the way in which your information is intercepted, it is common practice to intercept it via email or sms that are sent and ask you to visit the Organization's website, choosing a link included in the text (as shown in the image above). If you choose to visit the link, you will notice that this page simulates or completely copies familiar electronic environments, such as Piraeus Bank's online banking.

However, in no case is the "fake" environment an official page of the Organization you know. For your safety, it is recommended that you do not select the link and state your personal details and codes, as the experts will immediately proceed with transactions, causing you financial loss.

1903x750px blog post 01

In case you receive any suspicious email/sms, it is recommended not to enter the link that prompts you. Then, for your safety, you should immediately contact the Organization (in this case Piraeus Bank). In the event that the sender is Piraeus Bank, it is recommended that you call the 24-hour telephone service stating the incident. After reporting the incident and following the instructions of an authorized representative, you should delete the email or sms you have received, without forwarding it to anyone except to a competent Service of Piraeus Bank, if requested.

At this point, let us remind you that Piraeus Bank will never ask you in any way for the passwords to electronic banking services (winbank), or data and card codes, but will not proceed with a process of updating-verifying personal data, which excludes any possibility that the email or sms you received comes from Piraeus Bank.


Google preferences

Leave a Comment

Your email address will not be published. Required fields are marked *

Your message will not be published if:
1. Contains insulting, defamatory, racist, offensive or inappropriate comments.
2. Causes harm to minors.
3. It interferes with the privacy and individual and social rights of other users.
4. Advertises products or services or websites.
5. Contains personal information (address, phone, etc.).